
hi guys, I'm trying to create a certificate profile in a way to have at the end a certificate with a special attributes (supplied by the user through web enrollment form). I'm running dogtag 10.1 on Fedora 20...fresh install. I added a certificate profile using pkiconsole but I'm struggling in how to find the right Policies, Inputs and Outputs for the new profile. The OID I intent to write to it is the 2.16.76.1.3.3 (country specific OID). Here is my profile's config file: auth.instance_id= desc=UserCNPJ enable=false enableBy=admin input.CNPJ.class_id=genericInputImpl input.CNPJ.name=Generic Input input.CNPJ.params.gi_display_name0=Cadastro Nacional Pessoa Juridica input.CNPJ.params.gi_display_name1= input.CNPJ.params.gi_display_name2= input.CNPJ.params.gi_display_name3= input.CNPJ.params.gi_display_name4= input.CNPJ.params.gi_param_enable0=true input.CNPJ.params.gi_param_enable1=false input.CNPJ.params.gi_param_enable2=false input.CNPJ.params.gi_param_enable3=false input.CNPJ.params.gi_param_enable4=false input.CNPJ.params.gi_param_name0=cnpj input.CNPJ.params.gi_param_name1= input.CNPJ.params.gi_param_name2= input.CNPJ.params.gi_param_name3= input.CNPJ.params.gi_param_name4= input.i1.class_id=keyGenInputImpl input.i1.name=Key Generation Input input.i2.class_id=subjectNameInputImpl input.i2.name=Subject Name Input input.i3.class_id=submitterInfoInputImpl input.i3.name=Submitter Information Input input.list=i1,i2,i3,CNPJ input.params.gi_display_name0=Cadastro Nacional Pessoa Juridica input.params.gi_display_name1= input.params.gi_display_name2= input.params.gi_display_name3= input.params.gi_display_name4= input.params.gi_param_enable0=true input.params.gi_param_enable1=false input.params.gi_param_enable2=false input.params.gi_param_enable3=false input.params.gi_param_enable4=false input.params.gi_param_name0=cnpj input.params.gi_param_name1= input.params.gi_param_name2= input.params.gi_param_name3= input.params.gi_param_name4= lastModified=1390319210315 name=UserCNPJ output.list=o1 output.o1.class_id=certOutputImpl output.o1.name=Certificate Output policyset.list=set1 policyset.set1.list=p1,p2,p3,p4,p5,p06 policyset.set1.p06.constraint.class_id=noConstraintImpl policyset.set1.p06.constraint.name=No Constraint policyset.set1.p06.default.class_id=userExtensionDefaultImpl policyset.set1.p06.default.name=User Supplied Extension Default policyset.set1.p06.default.params.userExtOID=Comment Here... policyset.set1.p1.constraint.class_id=noConstraintImpl policyset.set1.p1.constraint.name=No Constraint policyset.set1.p1.default.class_id=userSubjectNameDefaultImpl policyset.set1.p1.default.name=User Supplied Subject Name Default policyset.set1.p2.constraint.class_id=noConstraintImpl policyset.set1.p2.constraint.name=No Constraint policyset.set1.p2.default.class_id=validityDefaultImpl policyset.set1.p2.default.name=Validity Default policyset.set1.p2.default.params.range=180 policyset.set1.p2.default.params.startTime=0 policyset.set1.p3.constraint.class_id=noConstraintImpl policyset.set1.p3.constraint.name=No Constraint policyset.set1.p3.default.class_id=userKeyDefaultImpl policyset.set1.p3.default.name=User Supplied Key Default policyset.set1.p3.default.params.keyMaxLength=4096 policyset.set1.p3.default.params.keyMinLength=512 policyset.set1.p3.default.params.keyType=RSA policyset.set1.p4.constraint.class_id=noConstraintImpl policyset.set1.p4.constraint.name=No Constraint policyset.set1.p4.default.class_id=signingAlgDefaultImpl policyset.set1.p4.default.name=Signing Algorithm Default policyset.set1.p4.default.params.signingAlg=- policyset.set1.p4.default.params.signingAlgsAllowed=SHA1withRSA,SHA256withRSA,SHA512withRSA,MD5withRSA,MD2withRSA,SHA1withEC,SHA256withEC,SHA384withEC,,SHA512withEC policyset.set1.p5.constraint.class_id=noConstraintImpl policyset.set1.p5.constraint.name=No Constraint policyset.set1.p5.default.class_id=keyUsageExtDefaultImpl policyset.set1.p5.default.name=Key Usage Extension Default policyset.set1.p5.default.params.keyUsageCritical=true policyset.set1.p5.default.params.keyUsageCrlSign=true policyset.set1.p5.default.params.keyUsageDataEncipherment=true policyset.set1.p5.default.params.keyUsageDecipherOnly=true policyset.set1.p5.default.params.keyUsageDigitalSignature=true policyset.set1.p5.default.params.keyUsageEncipherOnly=true policyset.set1.p5.default.params.keyUsageKeyAgreement=true policyset.set1.p5.default.params.keyUsageKeyCertSign=true policyset.set1.p5.default.params.keyUsageKeyEncipherment=true policyset.set1.p5.default.params.keyUsageNonRepudiation=true visible=true thx in advance, sergio

hi, have you tried something like this: policyset.set1.p6.constraint.class_id=noConstraintImpl policyset.set1.p6.constraint.name=No Constraint policyset.set1.p6.default.class_id=userExtensionDefaultImpl policyset.set1.p6.default.name=User Supplied Key Usage Extension policyset.set1.p6.default.params.userExtOID=2.16.76.1.3.3 jd On 01/22/2014 11:41 AM, Sergio Pereira wrote:
hi guys,
I'm trying to create a certificate profile in a way to have at the end a certificate with a special attributes (supplied by the user through web enrollment form). I'm running dogtag 10.1 on Fedora 20...fresh install. I added a certificate profile using pkiconsole but I'm struggling in how to find the right Policies, Inputs and Outputs for the new profile. The OID I intent to write to it is the 2.16.76.1.3.3 (country specific OID). Here is my profile's config file:
auth.instance_id= desc=UserCNPJ enable=false enableBy=admin input.CNPJ.class_id=genericInputImpl input.CNPJ.name <http://input.CNPJ.name>=Generic Input input.CNPJ.params.gi_display_name0=Cadastro Nacional Pessoa Juridica input.CNPJ.params.gi_display_name1= input.CNPJ.params.gi_display_name2= input.CNPJ.params.gi_display_name3= input.CNPJ.params.gi_display_name4= input.CNPJ.params.gi_param_enable0=true input.CNPJ.params.gi_param_enable1=false input.CNPJ.params.gi_param_enable2=false input.CNPJ.params.gi_param_enable3=false input.CNPJ.params.gi_param_enable4=false input.CNPJ.params.gi_param_name0=cnpj input.CNPJ.params.gi_param_name1= input.CNPJ.params.gi_param_name2= input.CNPJ.params.gi_param_name3= input.CNPJ.params.gi_param_name4= input.i1.class_id=keyGenInputImpl input.i1.name <http://input.i1.name>=Key Generation Input input.i2.class_id=subjectNameInputImpl input.i2.name <http://input.i2.name>=Subject Name Input input.i3.class_id=submitterInfoInputImpl input.i3.name <http://input.i3.name>=Submitter Information Input input.list=i1,i2,i3,CNPJ input.params.gi_display_name0=Cadastro Nacional Pessoa Juridica input.params.gi_display_name1= input.params.gi_display_name2= input.params.gi_display_name3= input.params.gi_display_name4= input.params.gi_param_enable0=true input.params.gi_param_enable1=false input.params.gi_param_enable2=false input.params.gi_param_enable3=false input.params.gi_param_enable4=false input.params.gi_param_name0=cnpj input.params.gi_param_name1= input.params.gi_param_name2= input.params.gi_param_name3= input.params.gi_param_name4= lastModified=1390319210315 name=UserCNPJ output.list=o1 output.o1.class_id=certOutputImpl output.o1.name <http://output.o1.name>=Certificate Output policyset.list=set1 policyset.set1.list=p1,p2,p3,p4,p5,p06 policyset.set1.p06.constraint.class_id=noConstraintImpl policyset.set1.p06.constraint.name <http://policyset.set1.p06.constraint.name>=No Constraint policyset.set1.p06.default.class_id=userExtensionDefaultImpl policyset.set1.p06.default.name <http://policyset.set1.p06.default.name>=User Supplied Extension Default policyset.set1.p06.default.params.userExtOID=Comment Here... policyset.set1.p1.constraint.class_id=noConstraintImpl policyset.set1.p1.constraint.name <http://policyset.set1.p1.constraint.name>=No Constraint policyset.set1.p1.default.class_id=userSubjectNameDefaultImpl policyset.set1.p1.default.name <http://policyset.set1.p1.default.name>=User Supplied Subject Name Default policyset.set1.p2.constraint.class_id=noConstraintImpl policyset.set1.p2.constraint.name <http://policyset.set1.p2.constraint.name>=No Constraint policyset.set1.p2.default.class_id=validityDefaultImpl policyset.set1.p2.default.name <http://policyset.set1.p2.default.name>=Validity Default policyset.set1.p2.default.params.range=180 policyset.set1.p2.default.params.startTime=0 policyset.set1.p3.constraint.class_id=noConstraintImpl policyset.set1.p3.constraint.name <http://policyset.set1.p3.constraint.name>=No Constraint policyset.set1.p3.default.class_id=userKeyDefaultImpl policyset.set1.p3.default.name <http://policyset.set1.p3.default.name>=User Supplied Key Default policyset.set1.p3.default.params.keyMaxLength=4096 policyset.set1.p3.default.params.keyMinLength=512 policyset.set1.p3.default.params.keyType=RSA policyset.set1.p4.constraint.class_id=noConstraintImpl policyset.set1.p4.constraint.name <http://policyset.set1.p4.constraint.name>=No Constraint policyset.set1.p4.default.class_id=signingAlgDefaultImpl policyset.set1.p4.default.name <http://policyset.set1.p4.default.name>=Signing Algorithm Default policyset.set1.p4.default.params.signingAlg=- policyset.set1.p4.default.params.signingAlgsAllowed=SHA1withRSA,SHA256withRSA,SHA512withRSA,MD5withRSA,MD2withRSA,SHA1withEC,SHA256withEC,SHA384withEC,,SHA512withEC policyset.set1.p5.constraint.class_id=noConstraintImpl policyset.set1.p5.constraint.name <http://policyset.set1.p5.constraint.name>=No Constraint policyset.set1.p5.default.class_id=keyUsageExtDefaultImpl policyset.set1.p5.default.name <http://policyset.set1.p5.default.name>=Key Usage Extension Default policyset.set1.p5.default.params.keyUsageCritical=true policyset.set1.p5.default.params.keyUsageCrlSign=true policyset.set1.p5.default.params.keyUsageDataEncipherment=true policyset.set1.p5.default.params.keyUsageDecipherOnly=true policyset.set1.p5.default.params.keyUsageDigitalSignature=true policyset.set1.p5.default.params.keyUsageEncipherOnly=true policyset.set1.p5.default.params.keyUsageKeyAgreement=true policyset.set1.p5.default.params.keyUsageKeyCertSign=true policyset.set1.p5.default.params.keyUsageKeyEncipherment=true policyset.set1.p5.default.params.keyUsageNonRepudiation=true visible=true thx in advance, sergio
_______________________________________________ Pki-users mailing list Pki-users@redhat.com https://www.redhat.com/mailman/listinfo/pki-users
</pre>****************************************************************************************<br>This email and any files transmitted with are confidential and intended solely for the<br>use of the individual or entity to whom they are addressed. If you have received this<br>email in error then please delete it and notify the sender. Do not make a copy or forward<br>it to anyone. This footnote also confirms that this email message has been swept for the<br>presence of computer viruses.<br><br>Adaptive Mobile Security Ltd, Ferry House, 48 Lower Mount Street, Dublin 2, Ireland<br>Directors: B. Collins, G. Maclachlan (UK), N. Grierson (UK), J. Ennis (UK), D. Summers (UK).<br>Registered in Ireland, Company No. 370343, VAT Reg.No.IE6390343O<br>****************************************************************************************</pre>
Hi JD, Just did it and I could sign the certificate. Any idea how to verify (list) the new OID info from a base64 cert? thx, sp 2014/1/22 Jindrich Dolezal <jindrich.dolezal@adaptivemobile.com>
hi, have you tried something like this: policyset.set1.p6.constraint.class_id=noConstraintImpl policyset.set1.p6.constraint.name=No Constraint policyset.set1.p6.default.class_id=userExtensionDefaultImpl policyset.set1.p6.default.name=User Supplied Key Usage Extension policyset.set1.p6.default.params.userExtOID=2.16.76.1.3.3
jd
On 01/22/2014 11:41 AM, Sergio Pereira wrote:
hi guys,
I'm trying to create a certificate profile in a way to have at the end a certificate with a special attributes (supplied by the user through web enrollment form). I'm running dogtag 10.1 on Fedora 20...fresh install. I added a certificate profile using pkiconsole but I'm struggling in how to find the right Policies, Inputs and Outputs for the new profile. The OID I intent to write to it is the 2.16.76.1.3.3 (country specific OID). Here is my profile's config file:
auth.instance_id= desc=UserCNPJ enable=false enableBy=admin input.CNPJ.class_id=genericInputImpl input.CNPJ.name=Generic Input input.CNPJ.params.gi_display_name0=Cadastro Nacional Pessoa Juridica input.CNPJ.params.gi_display_name1= input.CNPJ.params.gi_display_name2= input.CNPJ.params.gi_display_name3= input.CNPJ.params.gi_display_name4= input.CNPJ.params.gi_param_enable0=true input.CNPJ.params.gi_param_enable1=false input.CNPJ.params.gi_param_enable2=false input.CNPJ.params.gi_param_enable3=false input.CNPJ.params.gi_param_enable4=false input.CNPJ.params.gi_param_name0=cnpj input.CNPJ.params.gi_param_name1= input.CNPJ.params.gi_param_name2= input.CNPJ.params.gi_param_name3= input.CNPJ.params.gi_param_name4= input.i1.class_id=keyGenInputImpl input.i1.name=Key Generation Input input.i2.class_id=subjectNameInputImpl input.i2.name=Subject Name Input input.i3.class_id=submitterInfoInputImpl input.i3.name=Submitter Information Input input.list=i1,i2,i3,CNPJ input.params.gi_display_name0=Cadastro Nacional Pessoa Juridica input.params.gi_display_name1= input.params.gi_display_name2= input.params.gi_display_name3= input.params.gi_display_name4= input.params.gi_param_enable0=true input.params.gi_param_enable1=false input.params.gi_param_enable2=false input.params.gi_param_enable3=false input.params.gi_param_enable4=false input.params.gi_param_name0=cnpj input.params.gi_param_name1= input.params.gi_param_name2= input.params.gi_param_name3= input.params.gi_param_name4= lastModified=1390319210315 name=UserCNPJ output.list=o1 output.o1.class_id=certOutputImpl output.o1.name=Certificate Output policyset.list=set1 policyset.set1.list=p1,p2,p3,p4,p5,p06 policyset.set1.p06.constraint.class_id=noConstraintImpl policyset.set1.p06.constraint.name=No Constraint policyset.set1.p06.default.class_id=userExtensionDefaultImpl policyset.set1.p06.default.name=User Supplied Extension Default policyset.set1.p06.default.params.userExtOID=Comment Here... policyset.set1.p1.constraint.class_id=noConstraintImpl policyset.set1.p1.constraint.name=No Constraint policyset.set1.p1.default.class_id=userSubjectNameDefaultImpl policyset.set1.p1.default.name=User Supplied Subject Name Default policyset.set1.p2.constraint.class_id=noConstraintImpl policyset.set1.p2.constraint.name=No Constraint policyset.set1.p2.default.class_id=validityDefaultImpl policyset.set1.p2.default.name=Validity Default policyset.set1.p2.default.params.range=180 policyset.set1.p2.default.params.startTime=0 policyset.set1.p3.constraint.class_id=noConstraintImpl policyset.set1.p3.constraint.name=No Constraint policyset.set1.p3.default.class_id=userKeyDefaultImpl policyset.set1.p3.default.name=User Supplied Key Default policyset.set1.p3.default.params.keyMaxLength=4096 policyset.set1.p3.default.params.keyMinLength=512 policyset.set1.p3.default.params.keyType=RSA policyset.set1.p4.constraint.class_id=noConstraintImpl policyset.set1.p4.constraint.name=No Constraint policyset.set1.p4.default.class_id=signingAlgDefaultImpl policyset.set1.p4.default.name=Signing Algorithm Default policyset.set1.p4.default.params.signingAlg=-
policyset.set1.p4.default.params.signingAlgsAllowed=SHA1withRSA,SHA256withRSA,SHA512withRSA,MD5withRSA,MD2withRSA,SHA1withEC,SHA256withEC,SHA384withEC,,SHA512withEC policyset.set1.p5.constraint.class_id=noConstraintImpl policyset.set1.p5.constraint.name=No Constraint policyset.set1.p5.default.class_id=keyUsageExtDefaultImpl policyset.set1.p5.default.name=Key Usage Extension Default policyset.set1.p5.default.params.keyUsageCritical=true policyset.set1.p5.default.params.keyUsageCrlSign=true policyset.set1.p5.default.params.keyUsageDataEncipherment=true policyset.set1.p5.default.params.keyUsageDecipherOnly=true policyset.set1.p5.default.params.keyUsageDigitalSignature=true policyset.set1.p5.default.params.keyUsageEncipherOnly=true policyset.set1.p5.default.params.keyUsageKeyAgreement=true policyset.set1.p5.default.params.keyUsageKeyCertSign=true policyset.set1.p5.default.params.keyUsageKeyEncipherment=true policyset.set1.p5.default.params.keyUsageNonRepudiation=true visible=true
thx in advance, sergio
_______________________________________________ Pki-users mailing listPki-users@redhat.comhttps://www.redhat.com/mailman/listinfo/pki-users
</pre>****************************************************************************************<br>This email and any files transmitted with are confidential and intended solely for the<br>use of the individual or entity to whom they are addressed. If you have received this<br>email in error then please delete it and notify the sender. Do not make a copy or forward<br>it to anyone. This footnote also confirms that this email message has been swept for the<br>presence of computer viruses.<br><br>Adaptive Mobile Security Ltd, Ferry House, 48 Lower Mount Street, Dublin 2, Ireland<br>Directors: B. Collins, G. Maclachlan (UK), N. Grierson (UK), J. Ennis (UK), D. Summers (UK).<br>Registered in Ireland, Company No. 370343, VAT Reg.No.IE6390343O<br>****************************************************************************************</pre>
_______________________________________________ Pki-users mailing list Pki-users@redhat.com https://www.redhat.com/mailman/listinfo/pki-users
what about openssl x509 -in certificate.crt -text On 01/22/2014 01:07 PM, Sergio Pereira wrote:
Hi JD,
Just did it and I could sign the certificate. Any idea how to verify (list) the new OID info from a base64 cert? thx, sp
2014/1/22 Jindrich Dolezal <jindrich.dolezal@adaptivemobile.com <mailto:jindrich.dolezal@adaptivemobile.com>>
hi, have you tried something like this: policyset.set1.p6.constraint.class_id=noConstraintImpl policyset.set1.p6.constraint.name <http://policyset.set1.p6.constraint.name>=No Constraint policyset.set1.p6.default.class_id=userExtensionDefaultImpl policyset.set1.p6.default.name <http://policyset.set1.p6.default.name>=User Supplied Key Usage Extension policyset.set1.p6.default.params.userExtOID=2.16.76.1.3.3
jd
On 01/22/2014 11:41 AM, Sergio Pereira wrote:
hi guys,
I'm trying to create a certificate profile in a way to have at the end a certificate with a special attributes (supplied by the user through web enrollment form). I'm running dogtag 10.1 on Fedora 20...fresh install. I added a certificate profile using pkiconsole but I'm struggling in how to find the right Policies, Inputs and Outputs for the new profile. The OID I intent to write to it is the 2.16.76.1.3.3 (country specific OID). Here is my profile's config file:
auth.instance_id= desc=UserCNPJ enable=false enableBy=admin input.CNPJ.class_id=genericInputImpl input.CNPJ.name <http://input.CNPJ.name>=Generic Input input.CNPJ.params.gi_display_name0=Cadastro Nacional Pessoa Juridica input.CNPJ.params.gi_display_name1= input.CNPJ.params.gi_display_name2= input.CNPJ.params.gi_display_name3= input.CNPJ.params.gi_display_name4= input.CNPJ.params.gi_param_enable0=true input.CNPJ.params.gi_param_enable1=false input.CNPJ.params.gi_param_enable2=false input.CNPJ.params.gi_param_enable3=false input.CNPJ.params.gi_param_enable4=false input.CNPJ.params.gi_param_name0=cnpj input.CNPJ.params.gi_param_name1= input.CNPJ.params.gi_param_name2= input.CNPJ.params.gi_param_name3= input.CNPJ.params.gi_param_name4= input.i1.class_id=keyGenInputImpl input.i1.name <http://input.i1.name>=Key Generation Input input.i2.class_id=subjectNameInputImpl input.i2.name <http://input.i2.name>=Subject Name Input input.i3.class_id=submitterInfoInputImpl input.i3.name <http://input.i3.name>=Submitter Information Input input.list=i1,i2,i3,CNPJ input.params.gi_display_name0=Cadastro Nacional Pessoa Juridica input.params.gi_display_name1= input.params.gi_display_name2= input.params.gi_display_name3= input.params.gi_display_name4= input.params.gi_param_enable0=true input.params.gi_param_enable1=false input.params.gi_param_enable2=false input.params.gi_param_enable3=false input.params.gi_param_enable4=false input.params.gi_param_name0=cnpj input.params.gi_param_name1= input.params.gi_param_name2= input.params.gi_param_name3= input.params.gi_param_name4= lastModified=1390319210315 name=UserCNPJ output.list=o1 output.o1.class_id=certOutputImpl output.o1.name <http://output.o1.name>=Certificate Output policyset.list=set1 policyset.set1.list=p1,p2,p3,p4,p5,p06 policyset.set1.p06.constraint.class_id=noConstraintImpl policyset.set1.p06.constraint.name <http://policyset.set1.p06.constraint.name>=No Constraint policyset.set1.p06.default.class_id=userExtensionDefaultImpl policyset.set1.p06.default.name <http://policyset.set1.p06.default.name>=User Supplied Extension Default policyset.set1.p06.default.params.userExtOID=Comment Here... policyset.set1.p1.constraint.class_id=noConstraintImpl policyset.set1.p1.constraint.name <http://policyset.set1.p1.constraint.name>=No Constraint policyset.set1.p1.default.class_id=userSubjectNameDefaultImpl policyset.set1.p1.default.name <http://policyset.set1.p1.default.name>=User Supplied Subject Name Default policyset.set1.p2.constraint.class_id=noConstraintImpl policyset.set1.p2.constraint.name <http://policyset.set1.p2.constraint.name>=No Constraint policyset.set1.p2.default.class_id=validityDefaultImpl policyset.set1.p2.default.name <http://policyset.set1.p2.default.name>=Validity Default policyset.set1.p2.default.params.range=180 policyset.set1.p2.default.params.startTime=0 policyset.set1.p3.constraint.class_id=noConstraintImpl policyset.set1.p3.constraint.name <http://policyset.set1.p3.constraint.name>=No Constraint policyset.set1.p3.default.class_id=userKeyDefaultImpl policyset.set1.p3.default.name <http://policyset.set1.p3.default.name>=User Supplied Key Default policyset.set1.p3.default.params.keyMaxLength=4096 policyset.set1.p3.default.params.keyMinLength=512 policyset.set1.p3.default.params.keyType=RSA policyset.set1.p4.constraint.class_id=noConstraintImpl policyset.set1.p4.constraint.name <http://policyset.set1.p4.constraint.name>=No Constraint policyset.set1.p4.default.class_id=signingAlgDefaultImpl policyset.set1.p4.default.name <http://policyset.set1.p4.default.name>=Signing Algorithm Default policyset.set1.p4.default.params.signingAlg=- policyset.set1.p4.default.params.signingAlgsAllowed=SHA1withRSA,SHA256withRSA,SHA512withRSA,MD5withRSA,MD2withRSA,SHA1withEC,SHA256withEC,SHA384withEC,,SHA512withEC policyset.set1.p5.constraint.class_id=noConstraintImpl policyset.set1.p5.constraint.name <http://policyset.set1.p5.constraint.name>=No Constraint policyset.set1.p5.default.class_id=keyUsageExtDefaultImpl policyset.set1.p5.default.name <http://policyset.set1.p5.default.name>=Key Usage Extension Default policyset.set1.p5.default.params.keyUsageCritical=true policyset.set1.p5.default.params.keyUsageCrlSign=true policyset.set1.p5.default.params.keyUsageDataEncipherment=true policyset.set1.p5.default.params.keyUsageDecipherOnly=true policyset.set1.p5.default.params.keyUsageDigitalSignature=true policyset.set1.p5.default.params.keyUsageEncipherOnly=true policyset.set1.p5.default.params.keyUsageKeyAgreement=true policyset.set1.p5.default.params.keyUsageKeyCertSign=true policyset.set1.p5.default.params.keyUsageKeyEncipherment=true policyset.set1.p5.default.params.keyUsageNonRepudiation=true visible=true thx in advance, sergio
_______________________________________________ Pki-users mailing list Pki-users@redhat.com <mailto:Pki-users@redhat.com> https://www.redhat.com/mailman/listinfo/pki-users
</pre>****************************************************************************************<br>This email and any files transmitted with are confidential and intended solely for the<br>use of the individual or entity to whom they are addressed. If you have received this<br>email in error then please delete it and notify the sender. Do not make a copy or forward<br>it to anyone. This footnote also confirms that this email message has been swept for the<br>presence of computer viruses.<br><br>Adaptive Mobile Security Ltd, Ferry House, 48 Lower Mount Street, Dublin 2, Ireland<br>Directors: B. Collins, G. Maclachlan (UK), N. Grierson (UK), J. Ennis (UK), D. Summers (UK).<br>Registered in Ireland, Company No. 370343, VAT Reg.No.IE6390343O<br>****************************************************************************************</pre>
_______________________________________________ Pki-users mailing list Pki-users@redhat.com <mailto:Pki-users@redhat.com> https://www.redhat.com/mailman/listinfo/pki-users
</pre>****************************************************************************************<br>This email and any files transmitted with are confidential and intended solely for the<br>use of the individual or entity to whom they are addressed. If you have received this<br>email in error then please delete it and notify the sender. Do not make a copy or forward<br>it to anyone. This footnote also confirms that this email message has been swept for the<br>presence of computer viruses.<br><br>Adaptive Mobile Security Ltd, Ferry House, 48 Lower Mount Street, Dublin 2, Ireland<br>Directors: B. Collins, G. Maclachlan (UK), N. Grierson (UK), J. Ennis (UK), D. Summers (UK).<br>Registered in Ireland, Company No. 370343, VAT Reg.No.IE6390343O<br>****************************************************************************************</pre>
nope ... I see the x509 format certificate but can't see the new OID info. What I also did was to import the cert to a browser and checked the cert's details and also there is no new OID in it. sp 2014/1/22 Jindrich Dolezal <jindrich.dolezal@adaptivemobile.com>
what about openssl x509 -in certificate.crt -text
On 01/22/2014 01:07 PM, Sergio Pereira wrote:
Hi JD,
Just did it and I could sign the certificate. Any idea how to verify (list) the new OID info from a base64 cert? thx, sp
2014/1/22 Jindrich Dolezal <jindrich.dolezal@adaptivemobile.com>
hi, have you tried something like this: policyset.set1.p6.constraint.class_id=noConstraintImpl policyset.set1.p6.constraint.name=No Constraint policyset.set1.p6.default.class_id=userExtensionDefaultImpl policyset.set1.p6.default.name=User Supplied Key Usage Extension policyset.set1.p6.default.params.userExtOID=2.16.76.1.3.3
jd
On 01/22/2014 11:41 AM, Sergio Pereira wrote:
hi guys,
I'm trying to create a certificate profile in a way to have at the end a certificate with a special attributes (supplied by the user through web enrollment form). I'm running dogtag 10.1 on Fedora 20...fresh install. I added a certificate profile using pkiconsole but I'm struggling in how to find the right Policies, Inputs and Outputs for the new profile. The OID I intent to write to it is the 2.16.76.1.3.3 (country specific OID). Here is my profile's config file:
auth.instance_id= desc=UserCNPJ enable=false enableBy=admin input.CNPJ.class_id=genericInputImpl input.CNPJ.name=Generic Input input.CNPJ.params.gi_display_name0=Cadastro Nacional Pessoa Juridica input.CNPJ.params.gi_display_name1= input.CNPJ.params.gi_display_name2= input.CNPJ.params.gi_display_name3= input.CNPJ.params.gi_display_name4= input.CNPJ.params.gi_param_enable0=true input.CNPJ.params.gi_param_enable1=false input.CNPJ.params.gi_param_enable2=false input.CNPJ.params.gi_param_enable3=false input.CNPJ.params.gi_param_enable4=false input.CNPJ.params.gi_param_name0=cnpj input.CNPJ.params.gi_param_name1= input.CNPJ.params.gi_param_name2= input.CNPJ.params.gi_param_name3= input.CNPJ.params.gi_param_name4= input.i1.class_id=keyGenInputImpl input.i1.name=Key Generation Input input.i2.class_id=subjectNameInputImpl input.i2.name=Subject Name Input input.i3.class_id=submitterInfoInputImpl input.i3.name=Submitter Information Input input.list=i1,i2,i3,CNPJ input.params.gi_display_name0=Cadastro Nacional Pessoa Juridica input.params.gi_display_name1= input.params.gi_display_name2= input.params.gi_display_name3= input.params.gi_display_name4= input.params.gi_param_enable0=true input.params.gi_param_enable1=false input.params.gi_param_enable2=false input.params.gi_param_enable3=false input.params.gi_param_enable4=false input.params.gi_param_name0=cnpj input.params.gi_param_name1= input.params.gi_param_name2= input.params.gi_param_name3= input.params.gi_param_name4= lastModified=1390319210315 name=UserCNPJ output.list=o1 output.o1.class_id=certOutputImpl output.o1.name=Certificate Output policyset.list=set1 policyset.set1.list=p1,p2,p3,p4,p5,p06 policyset.set1.p06.constraint.class_id=noConstraintImpl policyset.set1.p06.constraint.name=No Constraint policyset.set1.p06.default.class_id=userExtensionDefaultImpl policyset.set1.p06.default.name=User Supplied Extension Default policyset.set1.p06.default.params.userExtOID=Comment Here... policyset.set1.p1.constraint.class_id=noConstraintImpl policyset.set1.p1.constraint.name=No Constraint policyset.set1.p1.default.class_id=userSubjectNameDefaultImpl policyset.set1.p1.default.name=User Supplied Subject Name Default policyset.set1.p2.constraint.class_id=noConstraintImpl policyset.set1.p2.constraint.name=No Constraint policyset.set1.p2.default.class_id=validityDefaultImpl policyset.set1.p2.default.name=Validity Default policyset.set1.p2.default.params.range=180 policyset.set1.p2.default.params.startTime=0 policyset.set1.p3.constraint.class_id=noConstraintImpl policyset.set1.p3.constraint.name=No Constraint policyset.set1.p3.default.class_id=userKeyDefaultImpl policyset.set1.p3.default.name=User Supplied Key Default policyset.set1.p3.default.params.keyMaxLength=4096 policyset.set1.p3.default.params.keyMinLength=512 policyset.set1.p3.default.params.keyType=RSA policyset.set1.p4.constraint.class_id=noConstraintImpl policyset.set1.p4.constraint.name=No Constraint policyset.set1.p4.default.class_id=signingAlgDefaultImpl policyset.set1.p4.default.name=Signing Algorithm Default policyset.set1.p4.default.params.signingAlg=-
policyset.set1.p4.default.params.signingAlgsAllowed=SHA1withRSA,SHA256withRSA,SHA512withRSA,MD5withRSA,MD2withRSA,SHA1withEC,SHA256withEC,SHA384withEC,,SHA512withEC policyset.set1.p5.constraint.class_id=noConstraintImpl policyset.set1.p5.constraint.name=No Constraint policyset.set1.p5.default.class_id=keyUsageExtDefaultImpl policyset.set1.p5.default.name=Key Usage Extension Default policyset.set1.p5.default.params.keyUsageCritical=true policyset.set1.p5.default.params.keyUsageCrlSign=true policyset.set1.p5.default.params.keyUsageDataEncipherment=true policyset.set1.p5.default.params.keyUsageDecipherOnly=true policyset.set1.p5.default.params.keyUsageDigitalSignature=true policyset.set1.p5.default.params.keyUsageEncipherOnly=true policyset.set1.p5.default.params.keyUsageKeyAgreement=true policyset.set1.p5.default.params.keyUsageKeyCertSign=true policyset.set1.p5.default.params.keyUsageKeyEncipherment=true policyset.set1.p5.default.params.keyUsageNonRepudiation=true visible=true
thx in advance, sergio
_______________________________________________ Pki-users mailing listPki-users@redhat.comhttps://www.redhat.com/mailman/listinfo/pki-users
</pre>****************************************************************************************<br>This email and any files transmitted with are confidential and intended solely for the<br>use of the individual or entity to whom they are addressed. If you have received this<br>email in error then please delete it and notify the sender. Do not make a copy or forward<br>it to anyone. This footnote also confirms that this email message has been swept for the<br>presence of computer viruses.<br><br>Adaptive Mobile Security Ltd, Ferry House, 48 Lower Mount Street, Dublin 2, Ireland<br>Directors: B. Collins, G. Maclachlan (UK), N. Grierson (UK), J. Ennis (UK), D. Summers (UK).<br>Registered in Ireland, Company No. 370343, VAT Reg.No.IE6390343O<br>****************************************************************************************</pre>
_______________________________________________ Pki-users mailing list Pki-users@redhat.com https://www.redhat.com/mailman/listinfo/pki-users
</pre>****************************************************************************************<br>This email and any files transmitted with are confidential and intended solely for the<br>use of the individual or entity to whom they are addressed. If you have received this<br>email in error then please delete it and notify the sender. Do not make a copy or forward<br>it to anyone. This footnote also confirms that this email message has been swept for the<br>presence of computer viruses.<br><br>Adaptive Mobile Security Ltd, Ferry House, 48 Lower Mount Street, Dublin 2, Ireland<br>Directors: B. Collins, G. Maclachlan (UK), N. Grierson (UK), J. Ennis (UK), D. Summers (UK).<br>Registered in Ireland, Company No. 370343, VAT Reg.No.IE6390343O<br>****************************************************************************************</pre>

Hi, If I understand it correctly, you just want the OID to appear in the cert? if so, Generic Extension might be what you are looking for: https://access.redhat.com/site/documentation/en-US/Red_Hat_Certificate_Syste... Here is an example of it: policyset.set1.p06.constraint.class_id=extensionConstraintImpl policyset.set1.p06.constraint.name=Extension Constraint policyset.set1.p06.constraint.params.extCritical=- policyset.set1.p06.constraint.params.extOID=2.16.76.1.3.3 policyset.set1.p06.default.class_id=userExtensionDefaultImpl policyset.set1.p06.default.name=Generic Extension Default policyset.set1.p06.default.params.genericExtData=bz policyset.set1.p06.default.params.genericExtOID=2.16.76.1.3.3 policyset.set1.p06.default.params.enericExtCritical=false In the above example, I just put your country OID in the profile, but I imagine you could change it to take it from the input. If you do so, you might want to lighten up on the constraint. I suggest you try the above hard-coded profile first just to see if the cert comes out what you are looking for before adding input in the profile. There is actually a bug in the GenericExtension area in regards to setting critical to true. I have yet to check the fix into Dogtag. Let me know if you do need that. BTW, regarding userExtensionDefault, it can only be used if your CSR has the wanted extension in the request already, so it's not going to help you. Hope this helps. Christina On 01/22/2014 02:41 AM, Sergio Pereira wrote:
hi guys,
I'm trying to create a certificate profile in a way to have at the end a certificate with a special attributes (supplied by the user through web enrollment form). I'm running dogtag 10.1 on Fedora 20...fresh install. I added a certificate profile using pkiconsole but I'm struggling in how to find the right Policies, Inputs and Outputs for the new profile. The OID I intent to write to it is the 2.16.76.1.3.3 (country specific OID). Here is my profile's config file:
auth.instance_id= desc=UserCNPJ enable=false enableBy=admin input.CNPJ.class_id=genericInputImpl input.CNPJ.name <http://input.CNPJ.name>=Generic Input input.CNPJ.params.gi_display_name0=Cadastro Nacional Pessoa Juridica input.CNPJ.params.gi_display_name1= input.CNPJ.params.gi_display_name2= input.CNPJ.params.gi_display_name3= input.CNPJ.params.gi_display_name4= input.CNPJ.params.gi_param_enable0=true input.CNPJ.params.gi_param_enable1=false input.CNPJ.params.gi_param_enable2=false input.CNPJ.params.gi_param_enable3=false input.CNPJ.params.gi_param_enable4=false input.CNPJ.params.gi_param_name0=cnpj input.CNPJ.params.gi_param_name1= input.CNPJ.params.gi_param_name2= input.CNPJ.params.gi_param_name3= input.CNPJ.params.gi_param_name4= input.i1.class_id=keyGenInputImpl input.i1.name <http://input.i1.name>=Key Generation Input input.i2.class_id=subjectNameInputImpl input.i2.name <http://input.i2.name>=Subject Name Input input.i3.class_id=submitterInfoInputImpl input.i3.name <http://input.i3.name>=Submitter Information Input input.list=i1,i2,i3,CNPJ input.params.gi_display_name0=Cadastro Nacional Pessoa Juridica input.params.gi_display_name1= input.params.gi_display_name2= input.params.gi_display_name3= input.params.gi_display_name4= input.params.gi_param_enable0=true input.params.gi_param_enable1=false input.params.gi_param_enable2=false input.params.gi_param_enable3=false input.params.gi_param_enable4=false input.params.gi_param_name0=cnpj input.params.gi_param_name1= input.params.gi_param_name2= input.params.gi_param_name3= input.params.gi_param_name4= lastModified=1390319210315 name=UserCNPJ output.list=o1 output.o1.class_id=certOutputImpl output.o1.name <http://output.o1.name>=Certificate Output policyset.list=set1 policyset.set1.list=p1,p2,p3,p4,p5,p06 policyset.set1.p06.constraint.class_id=noConstraintImpl policyset.set1.p06.constraint.name <http://policyset.set1.p06.constraint.name>=No Constraint policyset.set1.p06.default.class_id=userExtensionDefaultImpl policyset.set1.p06.default.name <http://policyset.set1.p06.default.name>=User Supplied Extension Default policyset.set1.p06.default.params.userExtOID=Comment Here... policyset.set1.p1.constraint.class_id=noConstraintImpl policyset.set1.p1.constraint.name <http://policyset.set1.p1.constraint.name>=No Constraint policyset.set1.p1.default.class_id=userSubjectNameDefaultImpl policyset.set1.p1.default.name <http://policyset.set1.p1.default.name>=User Supplied Subject Name Default policyset.set1.p2.constraint.class_id=noConstraintImpl policyset.set1.p2.constraint.name <http://policyset.set1.p2.constraint.name>=No Constraint policyset.set1.p2.default.class_id=validityDefaultImpl policyset.set1.p2.default.name <http://policyset.set1.p2.default.name>=Validity Default policyset.set1.p2.default.params.range=180 policyset.set1.p2.default.params.startTime=0 policyset.set1.p3.constraint.class_id=noConstraintImpl policyset.set1.p3.constraint.name <http://policyset.set1.p3.constraint.name>=No Constraint policyset.set1.p3.default.class_id=userKeyDefaultImpl policyset.set1.p3.default.name <http://policyset.set1.p3.default.name>=User Supplied Key Default policyset.set1.p3.default.params.keyMaxLength=4096 policyset.set1.p3.default.params.keyMinLength=512 policyset.set1.p3.default.params.keyType=RSA policyset.set1.p4.constraint.class_id=noConstraintImpl policyset.set1.p4.constraint.name <http://policyset.set1.p4.constraint.name>=No Constraint policyset.set1.p4.default.class_id=signingAlgDefaultImpl policyset.set1.p4.default.name <http://policyset.set1.p4.default.name>=Signing Algorithm Default policyset.set1.p4.default.params.signingAlg=- policyset.set1.p4.default.params.signingAlgsAllowed=SHA1withRSA,SHA256withRSA,SHA512withRSA,MD5withRSA,MD2withRSA,SHA1withEC,SHA256withEC,SHA384withEC,,SHA512withEC policyset.set1.p5.constraint.class_id=noConstraintImpl policyset.set1.p5.constraint.name <http://policyset.set1.p5.constraint.name>=No Constraint policyset.set1.p5.default.class_id=keyUsageExtDefaultImpl policyset.set1.p5.default.name <http://policyset.set1.p5.default.name>=Key Usage Extension Default policyset.set1.p5.default.params.keyUsageCritical=true policyset.set1.p5.default.params.keyUsageCrlSign=true policyset.set1.p5.default.params.keyUsageDataEncipherment=true policyset.set1.p5.default.params.keyUsageDecipherOnly=true policyset.set1.p5.default.params.keyUsageDigitalSignature=true policyset.set1.p5.default.params.keyUsageEncipherOnly=true policyset.set1.p5.default.params.keyUsageKeyAgreement=true policyset.set1.p5.default.params.keyUsageKeyCertSign=true policyset.set1.p5.default.params.keyUsageKeyEncipherment=true policyset.set1.p5.default.params.keyUsageNonRepudiation=true visible=true thx in advance, sergio
_______________________________________________ Pki-users mailing list Pki-users@redhat.com https://www.redhat.com/mailman/listinfo/pki-users
Hi Christina, I really appreciate for your response and time. I did try your suggestion but with no luck, when enrolling through web form I get the message: "Sorry, your request has been rejected. The reason is "Request Rejected - {0}". Attached is a picture of a real certificate, signed by a Brazilian CA and that is what I'm trying to accomplish using DogTag certificate system. The OID I'm trying to write to is marked in red and its value has some sort of Hex form (that would be the second step to be accomplished). One thing I realized is that the OID in question is in Subject Alternative Name and not as Generic Extension. thx, sp 2014/1/23 Christina Fu <cfu@redhat.com>
Hi,
If I understand it correctly, you just want the OID to appear in the cert? if so, Generic Extension might be what you are looking for:
https://access.redhat.com/site/documentation/en-US/Red_Hat_Certificate_Syste...
Here is an example of it: policyset.set1.p06.constraint.class_id=extensionConstraintImpl policyset.set1.p06.constraint.name=Extension Constraint policyset.set1.p06.constraint.params.extCritical=- policyset.set1.p06.constraint.params.extOID=2.16.76.1.3.3 policyset.set1.p06.default.class_id=userExtensionDefaultImpl policyset.set1.p06.default.name=Generic Extension Default policyset.set1.p06.default.params.genericExtData=bz policyset.set1.p06.default.params.genericExtOID=2.16.76.1.3.3 policyset.set1.p06.default.params.enericExtCritical=false
In the above example, I just put your country OID in the profile, but I imagine you could change it to take it from the input. If you do so, you might want to lighten up on the constraint. I suggest you try the above hard-coded profile first just to see if the cert comes out what you are looking for before adding input in the profile.
There is actually a bug in the GenericExtension area in regards to setting critical to true. I have yet to check the fix into Dogtag. Let me know if you do need that.
BTW, regarding userExtensionDefault, it can only be used if your CSR has the wanted extension in the request already, so it's not going to help you.
Hope this helps. Christina
On 01/22/2014 02:41 AM, Sergio Pereira wrote:
hi guys,
I'm trying to create a certificate profile in a way to have at the end a certificate with a special attributes (supplied by the user through web enrollment form). I'm running dogtag 10.1 on Fedora 20...fresh install. I added a certificate profile using pkiconsole but I'm struggling in how to find the right Policies, Inputs and Outputs for the new profile. The OID I intent to write to it is the 2.16.76.1.3.3 (country specific OID). Here is my profile's config file:
auth.instance_id= desc=UserCNPJ enable=false enableBy=admin input.CNPJ.class_id=genericInputImpl input.CNPJ.name=Generic Input input.CNPJ.params.gi_display_name0=Cadastro Nacional Pessoa Juridica input.CNPJ.params.gi_display_name1= input.CNPJ.params.gi_display_name2= input.CNPJ.params.gi_display_name3= input.CNPJ.params.gi_display_name4= input.CNPJ.params.gi_param_enable0=true input.CNPJ.params.gi_param_enable1=false input.CNPJ.params.gi_param_enable2=false input.CNPJ.params.gi_param_enable3=false input.CNPJ.params.gi_param_enable4=false input.CNPJ.params.gi_param_name0=cnpj input.CNPJ.params.gi_param_name1= input.CNPJ.params.gi_param_name2= input.CNPJ.params.gi_param_name3= input.CNPJ.params.gi_param_name4= input.i1.class_id=keyGenInputImpl input.i1.name=Key Generation Input input.i2.class_id=subjectNameInputImpl input.i2.name=Subject Name Input input.i3.class_id=submitterInfoInputImpl input.i3.name=Submitter Information Input input.list=i1,i2,i3,CNPJ input.params.gi_display_name0=Cadastro Nacional Pessoa Juridica input.params.gi_display_name1= input.params.gi_display_name2= input.params.gi_display_name3= input.params.gi_display_name4= input.params.gi_param_enable0=true input.params.gi_param_enable1=false input.params.gi_param_enable2=false input.params.gi_param_enable3=false input.params.gi_param_enable4=false input.params.gi_param_name0=cnpj input.params.gi_param_name1= input.params.gi_param_name2= input.params.gi_param_name3= input.params.gi_param_name4= lastModified=1390319210315 name=UserCNPJ output.list=o1 output.o1.class_id=certOutputImpl output.o1.name=Certificate Output policyset.list=set1 policyset.set1.list=p1,p2,p3,p4,p5,p06 policyset.set1.p06.constraint.class_id=noConstraintImpl policyset.set1.p06.constraint.name=No Constraint policyset.set1.p06.default.class_id=userExtensionDefaultImpl policyset.set1.p06.default.name=User Supplied Extension Default policyset.set1.p06.default.params.userExtOID=Comment Here... policyset.set1.p1.constraint.class_id=noConstraintImpl policyset.set1.p1.constraint.name=No Constraint policyset.set1.p1.default.class_id=userSubjectNameDefaultImpl policyset.set1.p1.default.name=User Supplied Subject Name Default policyset.set1.p2.constraint.class_id=noConstraintImpl policyset.set1.p2.constraint.name=No Constraint policyset.set1.p2.default.class_id=validityDefaultImpl policyset.set1.p2.default.name=Validity Default policyset.set1.p2.default.params.range=180 policyset.set1.p2.default.params.startTime=0 policyset.set1.p3.constraint.class_id=noConstraintImpl policyset.set1.p3.constraint.name=No Constraint policyset.set1.p3.default.class_id=userKeyDefaultImpl policyset.set1.p3.default.name=User Supplied Key Default policyset.set1.p3.default.params.keyMaxLength=4096 policyset.set1.p3.default.params.keyMinLength=512 policyset.set1.p3.default.params.keyType=RSA policyset.set1.p4.constraint.class_id=noConstraintImpl policyset.set1.p4.constraint.name=No Constraint policyset.set1.p4.default.class_id=signingAlgDefaultImpl policyset.set1.p4.default.name=Signing Algorithm Default policyset.set1.p4.default.params.signingAlg=-
policyset.set1.p4.default.params.signingAlgsAllowed=SHA1withRSA,SHA256withRSA,SHA512withRSA,MD5withRSA,MD2withRSA,SHA1withEC,SHA256withEC,SHA384withEC,,SHA512withEC policyset.set1.p5.constraint.class_id=noConstraintImpl policyset.set1.p5.constraint.name=No Constraint policyset.set1.p5.default.class_id=keyUsageExtDefaultImpl policyset.set1.p5.default.name=Key Usage Extension Default policyset.set1.p5.default.params.keyUsageCritical=true policyset.set1.p5.default.params.keyUsageCrlSign=true policyset.set1.p5.default.params.keyUsageDataEncipherment=true policyset.set1.p5.default.params.keyUsageDecipherOnly=true policyset.set1.p5.default.params.keyUsageDigitalSignature=true policyset.set1.p5.default.params.keyUsageEncipherOnly=true policyset.set1.p5.default.params.keyUsageKeyAgreement=true policyset.set1.p5.default.params.keyUsageKeyCertSign=true policyset.set1.p5.default.params.keyUsageKeyEncipherment=true policyset.set1.p5.default.params.keyUsageNonRepudiation=true visible=true
thx in advance, sergio
_______________________________________________ Pki-users mailing listPki-users@redhat.comhttps://www.redhat.com/mailman/listinfo/pki-users
_______________________________________________ Pki-users mailing list Pki-users@redhat.com https://www.redhat.com/mailman/listinfo/pki-users
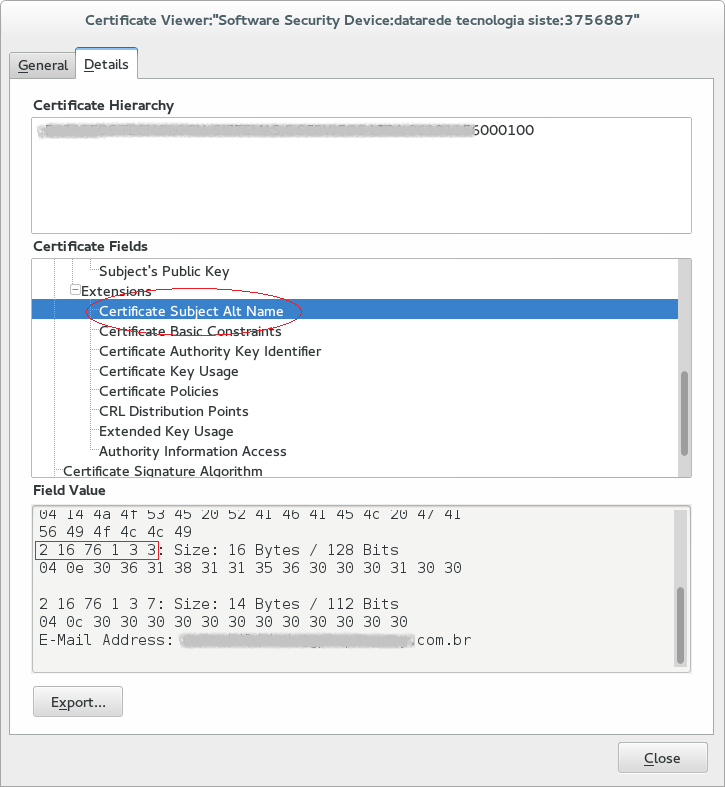
Hi Sergio, I did wonder if what you needed was Subject Alternative Name extension but since you said it's a "special attribute" I thought you want something different ;-). SubjectAlternativeName Extension is easy to apply in Dogtag. First, here is info regarding SubjectAlternativeName: https://access.redhat.com/site/documentation/en-US/Red_Hat_Certificate_Syste... Scroll down a page or two then you will find Table B.21 Subject Alternative Name extension Default Configuration Parameters. This is pretty much what you need. I think what you want for "Type" is "OIDName". So for example, you would have: policyset.set1.p06.constraint.class_id=noConstraintImpl policyset.set1.p06.constraint.name=No Constraint policyset.set1.p06.default.class_id=subjectAltNameExtDefaultImpl policyset.set1.p06.default.name=Subject Alternative Name Extension Default policyset.set1.p06.default.params.subjectAltNameExtCritical=false policyset.set1.p06.default.params.subjAltNameNumGNs=1 policyset.set1.p06.default.params.subjAltExtType_0=OIDName policyset.set1.p06.default.params.subjAltExtPattern_0=2.16.76.1.3.3 policyset.set1.p06.default.params.subjAltExtGNEnable_0=true again, the pattern part you can change it to take it from the input once it's working. However, unless you are in a controlled environment, it's better to have a constraint (You can write a plugin to suit your needs). And unless you have multiple OID's to insert, there is really no need to take from input. Regarding Generic Extension, I know it should work. Maybe your value did not match the constraint. But it's a moot point now since you are looking for SAN. hope this helps, Christina On 01/23/2014 04:12 AM, Sergio Pereira wrote:
Hi Christina,
I really appreciate for your response and time. I did try your suggestion but with no luck, when enrolling through web form I get the message: "Sorry, your request has been rejected. The reason is "Request Rejected - {0}". Attached is a picture of a real certificate, signed by a Brazilian CA and that is what I'm trying to accomplish using DogTag certificate system. The OID I'm trying to write to is marked in red and its value has some sort of Hex form (that would be the second step to be accomplished). One thing I realized is that the OID in question is in Subject Alternative Name and not as Generic Extension.
thx, sp
2014/1/23 Christina Fu <cfu@redhat.com <mailto:cfu@redhat.com>>
Hi,
If I understand it correctly, you just want the OID to appear in the cert? if so, Generic Extension might be what you are looking for: https://access.redhat.com/site/documentation/en-US/Red_Hat_Certificate_Syste...
Here is an example of it: policyset.set1.p06.constraint.class_id=extensionConstraintImpl policyset.set1.p06.constraint.name <http://policyset.set1.p06.constraint.name>=Extension Constraint policyset.set1.p06.constraint.params.extCritical=- policyset.set1.p06.constraint.params.extOID=2.16.76.1.3.3 policyset.set1.p06.default.class_id=userExtensionDefaultImpl policyset.set1.p06.default.name <http://policyset.set1.p06.default.name>=Generic Extension Default policyset.set1.p06.default.params.genericExtData=bz policyset.set1.p06.default.params.genericExtOID=2.16.76.1.3.3 policyset.set1.p06.default.params.enericExtCritical=false
In the above example, I just put your country OID in the profile, but I imagine you could change it to take it from the input. If you do so, you might want to lighten up on the constraint. I suggest you try the above hard-coded profile first just to see if the cert comes out what you are looking for before adding input in the profile.
There is actually a bug in the GenericExtension area in regards to setting critical to true. I have yet to check the fix into Dogtag. Let me know if you do need that.
BTW, regarding userExtensionDefault, it can only be used if your CSR has the wanted extension in the request already, so it's not going to help you.
Hope this helps. Christina
On 01/22/2014 02:41 AM, Sergio Pereira wrote:
hi guys,
I'm trying to create a certificate profile in a way to have at the end a certificate with a special attributes (supplied by the user through web enrollment form). I'm running dogtag 10.1 on Fedora 20...fresh install. I added a certificate profile using pkiconsole but I'm struggling in how to find the right Policies, Inputs and Outputs for the new profile. The OID I intent to write to it is the 2.16.76.1.3.3 (country specific OID). Here is my profile's config file:
auth.instance_id= desc=UserCNPJ enable=false enableBy=admin input.CNPJ.class_id=genericInputImpl input.CNPJ.name <http://input.CNPJ.name>=Generic Input input.CNPJ.params.gi_display_name0=Cadastro Nacional Pessoa Juridica input.CNPJ.params.gi_display_name1= input.CNPJ.params.gi_display_name2= input.CNPJ.params.gi_display_name3= input.CNPJ.params.gi_display_name4= input.CNPJ.params.gi_param_enable0=true input.CNPJ.params.gi_param_enable1=false input.CNPJ.params.gi_param_enable2=false input.CNPJ.params.gi_param_enable3=false input.CNPJ.params.gi_param_enable4=false input.CNPJ.params.gi_param_name0=cnpj input.CNPJ.params.gi_param_name1= input.CNPJ.params.gi_param_name2= input.CNPJ.params.gi_param_name3= input.CNPJ.params.gi_param_name4= input.i1.class_id=keyGenInputImpl input.i1.name <http://input.i1.name>=Key Generation Input input.i2.class_id=subjectNameInputImpl input.i2.name <http://input.i2.name>=Subject Name Input input.i3.class_id=submitterInfoInputImpl input.i3.name <http://input.i3.name>=Submitter Information Input input.list=i1,i2,i3,CNPJ input.params.gi_display_name0=Cadastro Nacional Pessoa Juridica input.params.gi_display_name1= input.params.gi_display_name2= input.params.gi_display_name3= input.params.gi_display_name4= input.params.gi_param_enable0=true input.params.gi_param_enable1=false input.params.gi_param_enable2=false input.params.gi_param_enable3=false input.params.gi_param_enable4=false input.params.gi_param_name0=cnpj input.params.gi_param_name1= input.params.gi_param_name2= input.params.gi_param_name3= input.params.gi_param_name4= lastModified=1390319210315 name=UserCNPJ output.list=o1 output.o1.class_id=certOutputImpl output.o1.name <http://output.o1.name>=Certificate Output policyset.list=set1 policyset.set1.list=p1,p2,p3,p4,p5,p06 policyset.set1.p06.constraint.class_id=noConstraintImpl policyset.set1.p06.constraint.name <http://policyset.set1.p06.constraint.name>=No Constraint policyset.set1.p06.default.class_id=userExtensionDefaultImpl policyset.set1.p06.default.name <http://policyset.set1.p06.default.name>=User Supplied Extension Default policyset.set1.p06.default.params.userExtOID=Comment Here... policyset.set1.p1.constraint.class_id=noConstraintImpl policyset.set1.p1.constraint.name <http://policyset.set1.p1.constraint.name>=No Constraint policyset.set1.p1.default.class_id=userSubjectNameDefaultImpl policyset.set1.p1.default.name <http://policyset.set1.p1.default.name>=User Supplied Subject Name Default policyset.set1.p2.constraint.class_id=noConstraintImpl policyset.set1.p2.constraint.name <http://policyset.set1.p2.constraint.name>=No Constraint policyset.set1.p2.default.class_id=validityDefaultImpl policyset.set1.p2.default.name <http://policyset.set1.p2.default.name>=Validity Default policyset.set1.p2.default.params.range=180 policyset.set1.p2.default.params.startTime=0 policyset.set1.p3.constraint.class_id=noConstraintImpl policyset.set1.p3.constraint.name <http://policyset.set1.p3.constraint.name>=No Constraint policyset.set1.p3.default.class_id=userKeyDefaultImpl policyset.set1.p3.default.name <http://policyset.set1.p3.default.name>=User Supplied Key Default policyset.set1.p3.default.params.keyMaxLength=4096 policyset.set1.p3.default.params.keyMinLength=512 policyset.set1.p3.default.params.keyType=RSA policyset.set1.p4.constraint.class_id=noConstraintImpl policyset.set1.p4.constraint.name <http://policyset.set1.p4.constraint.name>=No Constraint policyset.set1.p4.default.class_id=signingAlgDefaultImpl policyset.set1.p4.default.name <http://policyset.set1.p4.default.name>=Signing Algorithm Default policyset.set1.p4.default.params.signingAlg=- policyset.set1.p4.default.params.signingAlgsAllowed=SHA1withRSA,SHA256withRSA,SHA512withRSA,MD5withRSA,MD2withRSA,SHA1withEC,SHA256withEC,SHA384withEC,,SHA512withEC policyset.set1.p5.constraint.class_id=noConstraintImpl policyset.set1.p5.constraint.name <http://policyset.set1.p5.constraint.name>=No Constraint policyset.set1.p5.default.class_id=keyUsageExtDefaultImpl policyset.set1.p5.default.name <http://policyset.set1.p5.default.name>=Key Usage Extension Default policyset.set1.p5.default.params.keyUsageCritical=true policyset.set1.p5.default.params.keyUsageCrlSign=true policyset.set1.p5.default.params.keyUsageDataEncipherment=true policyset.set1.p5.default.params.keyUsageDecipherOnly=true policyset.set1.p5.default.params.keyUsageDigitalSignature=true policyset.set1.p5.default.params.keyUsageEncipherOnly=true policyset.set1.p5.default.params.keyUsageKeyAgreement=true policyset.set1.p5.default.params.keyUsageKeyCertSign=true policyset.set1.p5.default.params.keyUsageKeyEncipherment=true policyset.set1.p5.default.params.keyUsageNonRepudiation=true visible=true thx in advance, sergio
_______________________________________________ Pki-users mailing list Pki-users@redhat.com <mailto:Pki-users@redhat.com> https://www.redhat.com/mailman/listinfo/pki-users
_______________________________________________ Pki-users mailing list Pki-users@redhat.com <mailto:Pki-users@redhat.com> https://www.redhat.com/mailman/listinfo/pki-users
Hi Christina, Your help was just the key to find the right answer to my question. ;-) here is what I did to accomplish what I want: policyset.set1.p6.constraint.class_id=noConstraintImpl policyset.set1.p6.constraint.name=No Constraint policyset.set1.p6.default.class_id=subjectAltNameExtDefaultImpl policyset.set1.p6.default.name=Subject Alternative Name Extension Default policyset.set1.p6.default.params.subjAltExtGNEnable_0=true policyset.set1.p6.default.params.subjAltExtPattern_0=(PrintableString)2.16.76.1.3.3,$request.cnpj$ policyset.set1.p6.default.params.subjAltExtType_0=OtherName policyset.set1.p6.default.params.subjAltNameExtCritical=true policyset.set1.p6.default.params.subjAltNameNumGNs=1 worked like a charm ;-) thank you again. sp 2014-01-23 Christina Fu <cfu@redhat.com>
Hi Sergio,
I did wonder if what you needed was Subject Alternative Name extension but since you said it's a "special attribute" I thought you want something different ;-).
SubjectAlternativeName Extension is easy to apply in Dogtag.
First, here is info regarding SubjectAlternativeName:
https://access.redhat.com/site/documentation/en-US/Red_Hat_Certificate_Syste...
Scroll down a page or two then you will find Table B.21 Subject Alternative Name extension Default Configuration Parameters. This is pretty much what you need. I think what you want for "Type" is "OIDName".
So for example, you would have: policyset.set1.p06.constraint.class_id=noConstraintImpl policyset.set1.p06.constraint.name=No Constraint policyset.set1.p06.default.class_id=subjectAltNameExtDefaultImpl policyset.set1.p06.default.name=Subject Alternative Name Extension Default policyset.set1.p06.default.params.subjectAltNameExtCritical=false policyset.set1.p06.default.params.subjAltNameNumGNs=1 policyset.set1.p06.default.params.subjAltExtType_0=OIDName policyset.set1.p06.default.params.subjAltExtPattern_0=2.16.76.1.3.3 policyset.set1.p06.default.params.subjAltExtGNEnable_0=true
again, the pattern part you can change it to take it from the input once it's working. However, unless you are in a controlled environment, it's better to have a constraint (You can write a plugin to suit your needs). And unless you have multiple OID's to insert, there is really no need to take from input.
Regarding Generic Extension, I know it should work. Maybe your value did not match the constraint. But it's a moot point now since you are looking for SAN.
hope this helps, Christina
On 01/23/2014 04:12 AM, Sergio Pereira wrote:
Hi Christina,
I really appreciate for your response and time. I did try your suggestion but with no luck, when enrolling through web form I get the message: "Sorry, your request has been rejected. The reason is "Request Rejected - {0}". Attached is a picture of a real certificate, signed by a Brazilian CA and that is what I'm trying to accomplish using DogTag certificate system. The OID I'm trying to write to is marked in red and its value has some sort of Hex form (that would be the second step to be accomplished). One thing I realized is that the OID in question is in Subject Alternative Name and not as Generic Extension.
thx, sp
2014/1/23 Christina Fu <cfu@redhat.com>
Hi,
If I understand it correctly, you just want the OID to appear in the cert? if so, Generic Extension might be what you are looking for:
https://access.redhat.com/site/documentation/en-US/Red_Hat_Certificate_Syste...
Here is an example of it: policyset.set1.p06.constraint.class_id=extensionConstraintImpl policyset.set1.p06.constraint.name=Extension Constraint policyset.set1.p06.constraint.params.extCritical=- policyset.set1.p06.constraint.params.extOID=2.16.76.1.3.3 policyset.set1.p06.default.class_id=userExtensionDefaultImpl policyset.set1.p06.default.name=Generic Extension Default policyset.set1.p06.default.params.genericExtData=bz policyset.set1.p06.default.params.genericExtOID=2.16.76.1.3.3 policyset.set1.p06.default.params.enericExtCritical=false
In the above example, I just put your country OID in the profile, but I imagine you could change it to take it from the input. If you do so, you might want to lighten up on the constraint. I suggest you try the above hard-coded profile first just to see if the cert comes out what you are looking for before adding input in the profile.
There is actually a bug in the GenericExtension area in regards to setting critical to true. I have yet to check the fix into Dogtag. Let me know if you do need that.
BTW, regarding userExtensionDefault, it can only be used if your CSR has the wanted extension in the request already, so it's not going to help you.
Hope this helps. Christina
On 01/22/2014 02:41 AM, Sergio Pereira wrote:
hi guys,
I'm trying to create a certificate profile in a way to have at the end a certificate with a special attributes (supplied by the user through web enrollment form). I'm running dogtag 10.1 on Fedora 20...fresh install. I added a certificate profile using pkiconsole but I'm struggling in how to find the right Policies, Inputs and Outputs for the new profile. The OID I intent to write to it is the 2.16.76.1.3.3 (country specific OID). Here is my profile's config file:
auth.instance_id= desc=UserCNPJ enable=false enableBy=admin input.CNPJ.class_id=genericInputImpl input.CNPJ.name=Generic Input input.CNPJ.params.gi_display_name0=Cadastro Nacional Pessoa Juridica input.CNPJ.params.gi_display_name1= input.CNPJ.params.gi_display_name2= input.CNPJ.params.gi_display_name3= input.CNPJ.params.gi_display_name4= input.CNPJ.params.gi_param_enable0=true input.CNPJ.params.gi_param_enable1=false input.CNPJ.params.gi_param_enable2=false input.CNPJ.params.gi_param_enable3=false input.CNPJ.params.gi_param_enable4=false input.CNPJ.params.gi_param_name0=cnpj input.CNPJ.params.gi_param_name1= input.CNPJ.params.gi_param_name2= input.CNPJ.params.gi_param_name3= input.CNPJ.params.gi_param_name4= input.i1.class_id=keyGenInputImpl input.i1.name=Key Generation Input input.i2.class_id=subjectNameInputImpl input.i2.name=Subject Name Input input.i3.class_id=submitterInfoInputImpl input.i3.name=Submitter Information Input input.list=i1,i2,i3,CNPJ input.params.gi_display_name0=Cadastro Nacional Pessoa Juridica input.params.gi_display_name1= input.params.gi_display_name2= input.params.gi_display_name3= input.params.gi_display_name4= input.params.gi_param_enable0=true input.params.gi_param_enable1=false input.params.gi_param_enable2=false input.params.gi_param_enable3=false input.params.gi_param_enable4=false input.params.gi_param_name0=cnpj input.params.gi_param_name1= input.params.gi_param_name2= input.params.gi_param_name3= input.params.gi_param_name4= lastModified=1390319210315 name=UserCNPJ output.list=o1 output.o1.class_id=certOutputImpl output.o1.name=Certificate Output policyset.list=set1 policyset.set1.list=p1,p2,p3,p4,p5,p06 policyset.set1.p06.constraint.class_id=noConstraintImpl policyset.set1.p06.constraint.name=No Constraint policyset.set1.p06.default.class_id=userExtensionDefaultImpl policyset.set1.p06.default.name=User Supplied Extension Default policyset.set1.p06.default.params.userExtOID=Comment Here... policyset.set1.p1.constraint.class_id=noConstraintImpl policyset.set1.p1.constraint.name=No Constraint policyset.set1.p1.default.class_id=userSubjectNameDefaultImpl policyset.set1.p1.default.name=User Supplied Subject Name Default policyset.set1.p2.constraint.class_id=noConstraintImpl policyset.set1.p2.constraint.name=No Constraint policyset.set1.p2.default.class_id=validityDefaultImpl policyset.set1.p2.default.name=Validity Default policyset.set1.p2.default.params.range=180 policyset.set1.p2.default.params.startTime=0 policyset.set1.p3.constraint.class_id=noConstraintImpl policyset.set1.p3.constraint.name=No Constraint policyset.set1.p3.default.class_id=userKeyDefaultImpl policyset.set1.p3.default.name=User Supplied Key Default policyset.set1.p3.default.params.keyMaxLength=4096 policyset.set1.p3.default.params.keyMinLength=512 policyset.set1.p3.default.params.keyType=RSA policyset.set1.p4.constraint.class_id=noConstraintImpl policyset.set1.p4.constraint.name=No Constraint policyset.set1.p4.default.class_id=signingAlgDefaultImpl policyset.set1.p4.default.name=Signing Algorithm Default policyset.set1.p4.default.params.signingAlg=-
policyset.set1.p4.default.params.signingAlgsAllowed=SHA1withRSA,SHA256withRSA,SHA512withRSA,MD5withRSA,MD2withRSA,SHA1withEC,SHA256withEC,SHA384withEC,,SHA512withEC policyset.set1.p5.constraint.class_id=noConstraintImpl policyset.set1.p5.constraint.name=No Constraint policyset.set1.p5.default.class_id=keyUsageExtDefaultImpl policyset.set1.p5.default.name=Key Usage Extension Default policyset.set1.p5.default.params.keyUsageCritical=true policyset.set1.p5.default.params.keyUsageCrlSign=true policyset.set1.p5.default.params.keyUsageDataEncipherment=true policyset.set1.p5.default.params.keyUsageDecipherOnly=true policyset.set1.p5.default.params.keyUsageDigitalSignature=true policyset.set1.p5.default.params.keyUsageEncipherOnly=true policyset.set1.p5.default.params.keyUsageKeyAgreement=true policyset.set1.p5.default.params.keyUsageKeyCertSign=true policyset.set1.p5.default.params.keyUsageKeyEncipherment=true policyset.set1.p5.default.params.keyUsageNonRepudiation=true visible=true
thx in advance, sergio
_______________________________________________ Pki-users mailing listPki-users@redhat.comhttps://www.redhat.com/mailman/listinfo/pki-users
_______________________________________________ Pki-users mailing list Pki-users@redhat.com https://www.redhat.com/mailman/listinfo/pki-users
_______________________________________________ Pki-users mailing list Pki-users@redhat.com https://www.redhat.com/mailman/listinfo/pki-users
participants (3)
-
 Christina Fu
-
 Jindrich Dolezal
-
 Sergio Pereira